Background
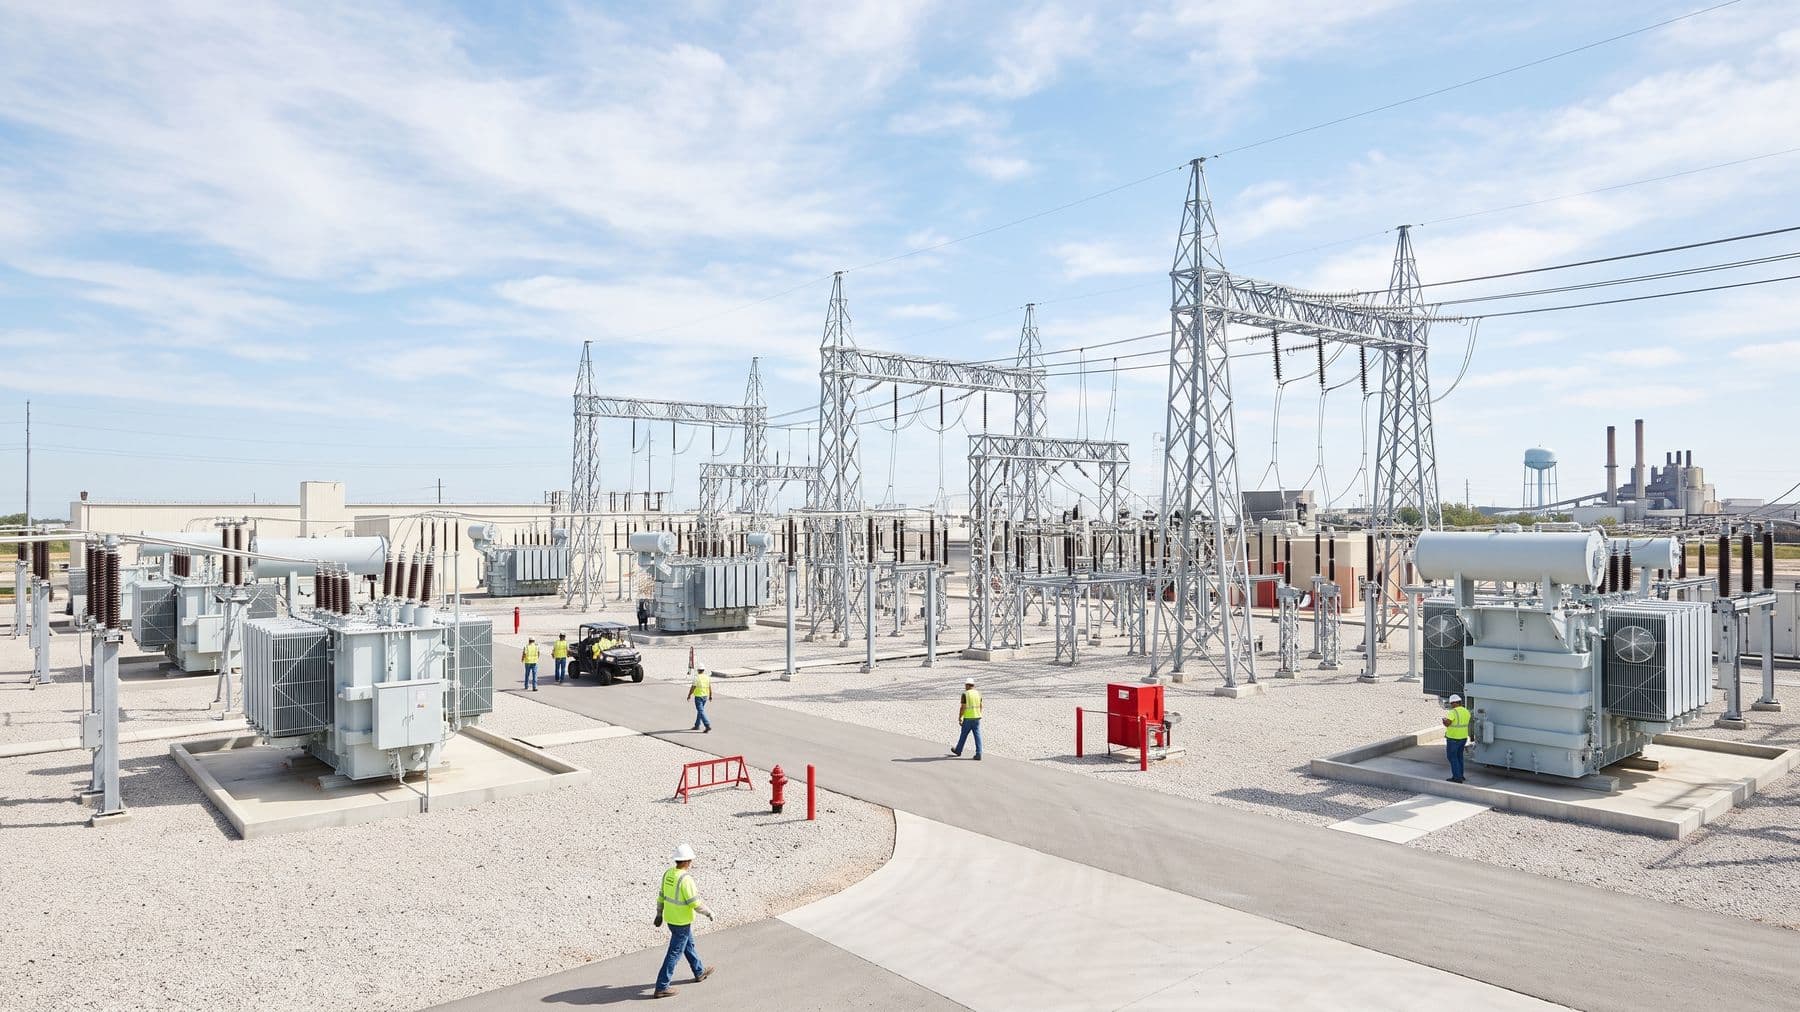
An important urban utility with a strong reputation for reliability contacted ACS after its largest plant shut down because of an electronic connection to one of its vendors. The utility's vendor required the connection to maintain its warranty on critical infrastructure and also to address the security requirements of the North American Electric Reliability Corporation's (NERC's) Critical Infrastructure Protection (CIP). The utility needed a practical way to resolve the immediate issue while strengthening reliability and security policies across both electric and water operations.
The Challenge
The broader challenge was not simply an IP-network cybersecurity problem. ACS, led by Joe Weiss, brought specialized expertise in non-IP industrial control system (ICS) failures: events in which control systems or the physical processes they manage are affected unrelated to the kinds of IP-network cyberattacks that dominate most security and safety thinking and planning. Weiss has tracked these incidents for more than 20 years. He has catalogued control-system and process-impacting events causing tens of thousands of fatalities and more than $100 billion in damage, while showing that virtually all of the most consequential incidents did not involve the IP-network attack paths on which industry and government have focused so much attention.
This created a strategic insight for the utility and for the industry more broadly: organizations had been investing heavily in the visible problem of network cybersecurity while missing the engineering-based, physics-based, non-IP failure modes that create real-world consequences. In short, the industry was solving the wrong problem, or at least a very incomplete one.
ACS Approach
ACS helped the utility as a subject matter expert develop security and safety policies for its electric and water operations and reframe the problem around operational impact rather than network exposure alone. Working with a division of the Department of Defense, ACS helped establish a joint working relationship with BWP on a class of control-system risk with damaging physical effects not present in conventional IP-network attacks. This collaboration evolved into the utility becoming one of only two utility test sites in the United States and later expanded into a control-system security and safety testbed.
ACS worked collaboratively with the utility to encourage its vendors to test their products at the site. This helped move the discussion beyond compliance and into practical validation of control-system behavior under realistic operating conditions. ACS also supported the utility in addressing supply-chain and assurance concerns when software for a new distribution SCADA system originated from outside the traditional Western software ecosystem.
Results and Impact
The collaboration produced results well beyond the utility's immediate operational needs. It contributed to industry awareness of this persistent class of control-system risk through press coverage, presentations at ICS conferences, and a television special. More importantly, the work demonstrated how utilities can use engineering expertise, operational testing, and control-system incident history to identify risks that conventional cybersecurity programs overlook.
Key Lesson
The experience of this utility illustrates why ICS cybersecurity must include more than IP-network defenses. The most consequential failures arise instead from control logic, instrumentation, timing, vendor dependencies, engineering assumptions, physics-layer behavior, and other non-IP pathways. ACS helped this utility address these risks by applying more than two decades of control-system incident analysis to their real operational environment. The result was a stronger, more realistic view of security: one grounded not only in networks, but in the physical systems that keep critical infrastructure running.